
 0


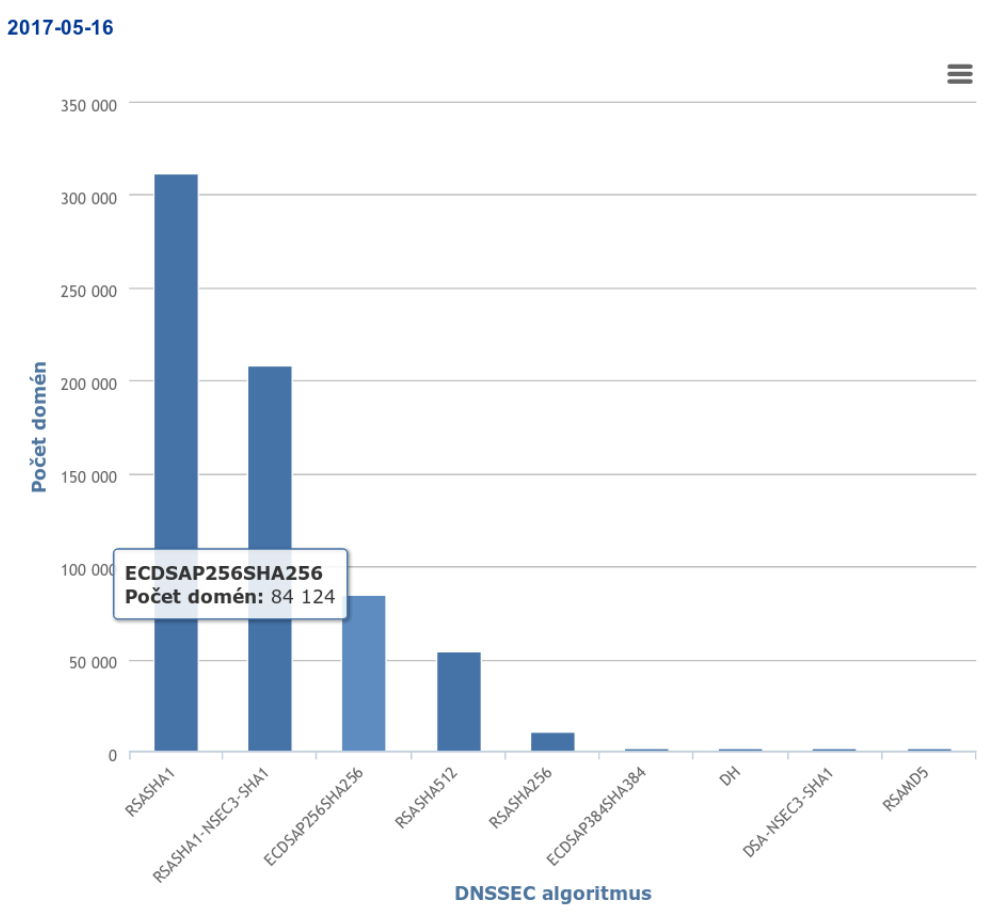
The statistics show that RSASHA1 is still the most widely used algorithm. Unfortunately, this algorithm has a number of disadvantages. The main problem is its incompatibility with the NSEC3 technology and therefore it is primarily intended for zones where their content being publicly available is not an issue. The second disadvantage is its use of the “obsolete” hash function SHA1. Therefore, it is important that domain administrators using this algorithm for DNSSEC consider switching to another type of algorithm. We are happy to observe that the ECDSA algorithm is definitely nothing rare in the .cz zone. It is currently used by over 80,000 domains; that is almost 13%, which makes it the third most used DNSSEC algorithm. How we got there is shown in the following chart.
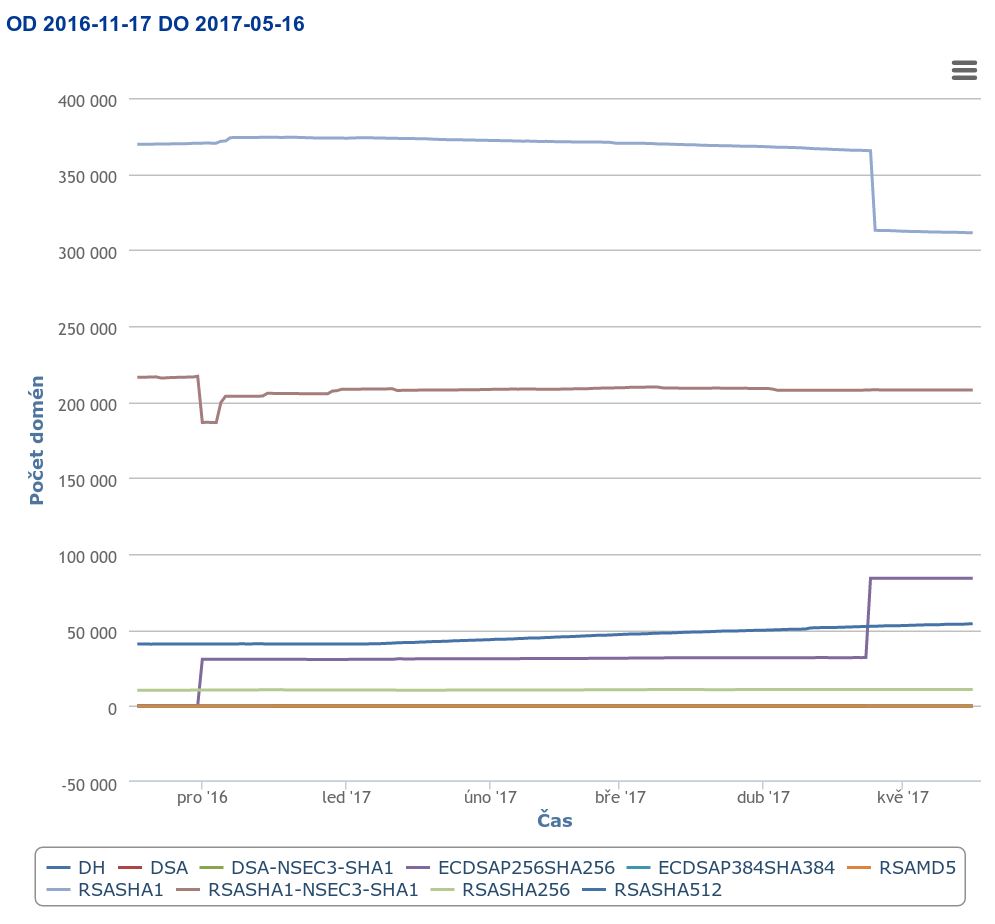
The development of support for the algorithm referred to as ECDSAP256SHA256 can be seen on the purple curve. By December 2016, it was supported by a few hundred domains. This includes about a hundred of our own domains, and the rest are Cloudflare infrastructure based domains. This company is the world’s leader in ECDSA support. It has several thousand domains in our country, however due to the non-existent link between DNS operators and registrars, not all of them have DNSSEC. This could change with the automated key set management project we are currently working on.
In December 2016, the chart shows the first big leap caused by the shift to ECDSA of all domains hosted by the Zoner registrar, which included about 30,000 domains. The chart also shows that it was a transition from the RSASHA1-NSEC3-SHA1 algorithm. The second big leap occurred two weeks ago, when the IGNUM registrar transferred all of its domains to ECDSA in a similar way. This time it was over 50,000 domains and it was at the expense of the RSASHA1 algorithm. Both registrars have described this transition as seamless. Of course, we are pleased that among our registrars there are also those who can manage a not quite trivial rotation of DNSSEC keys. Changing the algorithm is not the same as a common key change, as it requires more steps and more attention. We will try to get a more detailed report from them, perhaps already at the IT 17 conference in June.